Hackers Exploit Security Weaknesses in Domain Systems to Pose as Google Over HTTPS
Attackers have taken advantage of flaws in the domain infrastructure to generate fake HTTPS certificates for certain Google sites, putting online security at risk.
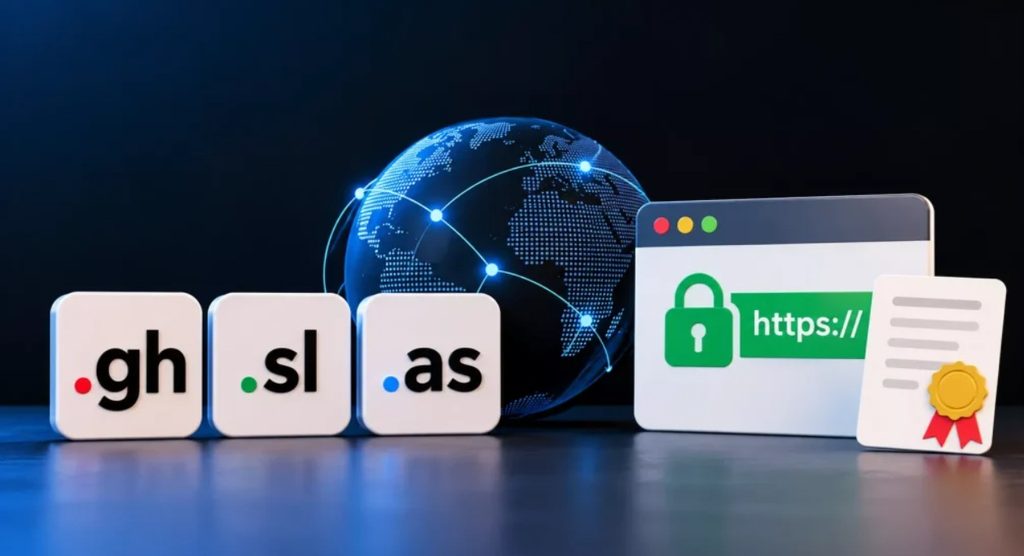
The attackers‘ operations relied on the domain infrastructure of Ghana, Sierra Leone, and American Samoa; by controlling these infrastructures, the attackers posed as certificate authorities and obtained the ability to create and distribute fraudulent certificates for Google and other sites.
Certificates of this kind are generally used to confirm that a website is legitimate and to safeguard data entered into forms and other website functions.
It is worth stressing that Google itself was not hacked; instead, the attackers managed to infiltrate and seize control of certificate authorities responsible for issuing certificates in the domains mentioned at the start of the article.
Google Responds to Protect Its Users
Once the fraud was detected, Google blocked the certificates and collaborated with the owners of the certificate-issuing companies to have them revoked.
Google also noted that it does not think its users’ security would be compromised, since the attackers were unlikely to have been able to intercept any encrypted communications.
In addition, Google reported other certificates issued to different companies that were also affected by the attack.
This issue requires no action from end-users, since Google has implemented measures within the Chrome browser to ensure that fraudulent certificates will not be recognized.
At the same time, this attack once again underscores the importance of protecting the network infrastructure and domain name system, which is highly attractive to attackers.
Attackers frequently seek ways to undermine an organization’s security by inserting themselves into the network and exploiting the resources available there.
Google itself is investigating the attack and has urged website owners to make sure they are not vulnerable to the creation of rogue certificates.
This attack is merely one example of how the security of companies and organizations can be threatened, even when their own IT infrastructure is protected from external interference.
The reason for this threat lies in the weak protection of certain elements of the network infrastructure on which all IT systems and online services depend.
This is exactly why companies and organizations must carefully monitor every area of their operation in order to quickly detect and neutralize potential security threats.
As a rule, such threats can be eliminated if they are detected in time, whereas delayed or absent responses may allow attackers to benefit considerably from the situation.