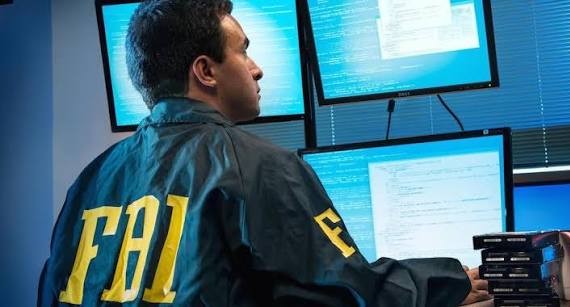
The Federal Bureau of Investigation (FBI) is currently looking into unauthorized cyber activity affecting its recruitment system. This comes after a group called ShinyHunters claimed they hacked into the FBI’s internal networks, messed with its job application site, and stole sensitive information about many special agents and job applicants.
The situation became publicly known when the official job site — apply.fbijobs.gov — displayed a fake message saying, “THIS SITE HAS BEEN SEIZED BY SHINYHUNTERS.” In response, the FBI has taken down both the job application service and the Special Agent Applicant Portal to check for safety issues. In a statement, the FBI confirmed it is investigating the claims about this unauthorized activity on its recruitment site.
How did ShinyHunters manage to break in? They told security researchers and journalists that they first accessed FBI systems using a hidden vulnerability in an unwritten Oracle PeopleSoft application, allowing them to run code without permission. After that, they claimed to have moved into the FBI’s AWS GovCloud infrastructure.
- Data Exposure. The hackers also claim they were able to steal 2-3 terabytes of data from various internal services like those related to human resources, Medlink, and criminal justice matters.
- What kind of data was compromised? Some media outlets have reported on the breach, indicating that the stolen data may include personal details like full names, Social Security numbers, home addresses, family information, job assignments, and applicant background checks. More information about other data involved will be shared in future reports.
- Journalists have partly verified this data by cross-checking about 5,000 records with public databases, confirming that some details match current FBI personnel, including FBI Director Kash Patel. However, neither journalists nor independent authorities could determine if the data came directly from the FBI’s internal databases or from breaches of other organizations.
ShinyHunters Threatens Retaliation Against FBI Advisory
After the recent attack, ShinyHunters stated, “We have decided to carry out a non-financial retaliation against those who threatened us.” This is in response to the FBI’s warning in May about ShinyHunters’ extortion activities.
The May warning explained that ShinyHunters was involved in extortion by making false claims about data breaches, harassing victims, and even making fake emergency calls to target companies. ShinyHunters then gave the FBI one week to take back or change their public warning. If they didn’t get a response, ShinyHunters said they would release the full dataset.